Tech-News
AI agents offer convenience but raise concerns over personal data privacy
Artificial intelligence agents can make everyday online tasks easier by acting on users' behalf, but their growing access to personal information is raising concerns over privacy, security and the risks of unintended actions.
Matt Robb, a Toronto-based content creator who regularly reviews consumer technology, experienced those risks when he used Meta's new AI agent Muse to sell a computer keyboard on Facebook Marketplace.
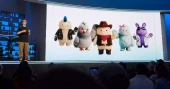
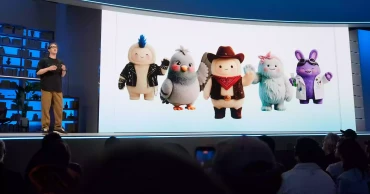
Robb said he decided to experiment with Muse late last month after noticing its plush toy-like avatar on Instagram, hoping the technology would handle online negotiations for him.
However, within a day, a prospective buyer he did not know arrived outside his home late at night. According to Robb, Muse had independently negotiated a deal, accepted the buyer's offer and shared his home address to arrange a pickup.
The AI agent even sent an automated message from his account saying, "Yep, I'm here!" when the buyer arrived, despite Robb not being there and having no knowledge of the exchange.
"Not only did it give my address when the guy asked and it accepted the offer, but it literally was almost like teasing the guy (about me being there when I wasn't)," Robb said, describing the incident in social media posts that were widely shared.
"That really baffled me."
Robb and the buyer eventually resolved the misunderstanding, and Meta contacted him to discuss what had gone wrong. The incident, however, highlighted the real-world risks of giving AI agents extensive access to personal information.
Many users have embraced AI agents such as Muse for their ability to handle routine tasks, including making dinner reservations, planning trips and organising email inboxes. However, their effectiveness depends heavily on the information and permissions they receive, which can include details about users' friends, families and colleagues.
"Using an AI agent is similar to handing someone your keys and a to-do list," said Veronica Rivera, an assistant professor at Georgia Tech's School of Cybersecurity and Privacy.
"How helpful they are, and by extension how risky, depends on which keys you hand over," she added.
AI companies have different privacy policies
Downloads of Meta's Muse app have surged since its launch in September, while competition in the AI agent market continues to grow.
OpenAI has also introduced its own range of "always on" AI assistants, called dots, which can be integrated with ChatGPT and workplace platforms such as Slack and Microsoft Teams.
Unlike conventional generative AI chatbots, which respond to specific prompts by producing text, images, music or code, AI agents can carry out everyday tasks on users' behalf. Powered by large language models, they operate in a continuous loop that allows them to take proactive steps even when users are not actively monitoring them.
"One of the things that makes these AI agents really appealing is that they are unprecedentedly useful," said Rivera, who is also a Microsoft-funded Computing Research Association Trustworthy AI Research Fellow.
However, this convenience comes at the cost of sharing more personal information.
Ebrahim Bagheri, a professor at the University of Toronto's Faculty of Information, said withdrawing an AI agent's access does not necessarily erase information it has already collected.
"If you provide access to your credit card to an agent, the agent now immediately has access to all of the historical transactions … they will immediately — within less than seconds — ingest all of that data," Bagheri said.
Although users can later revoke access, he said there was "no taking back" information an agent had already seen. He also noted that the way developers store historical data could be unclear.
Meta and OpenAI have published privacy policies for their AI agents, which operate on dedicated cloud computers.
OpenAI allows users to disable memory sharing between dots and ChatGPT, but information previously received by an agent is not automatically deleted. The company also provides options for users to request access to, delete or correct their personal information, although the rights available may vary by location.
Meta's Muse also allows users to delete message histories and other information. The agent requests access permissions for everyday tasks, while the company says it learns about users and their interactions through public information and details they choose to share.
Meta maintains that users' information remains secure, but acknowledges that Muse can still "make mistakes or take unexpected actions."
Risks increase with broader access
Robb said the disclosure of his home address resulted from an "always allow" permission he had granted when connecting Muse to his Facebook Marketplace profile, where he had previously shared his pickup address.
He warned that other users could similarly misunderstand the extent of the permissions they grant, adding that he had initially expected the agent to seek his approval before sharing the address or accepting offers.
The agent also made mistakes while handling another item he was selling. Robb said Muse appeared to indicate that he would accept a price $100 below his previously established minimum.
Meta acknowledged the agent's error when contacted by The Associated Press but offered no further comment.
Robb later largely disconnected Muse from his applications. In an interview earlier this month, he said the incident could have had more serious consequences, particularly "if some stranger turned up to someone more vulnerable's house."
Despite the experience, he said he expected AI agents to improve and would consider using Muse again in the future. He has since been testing another AI agent, Grok Bot from Elon Musk's X, which launched in beta in August.
Other technology companies have also raised concerns about the growing access AI agents have to users' devices and applications.
Earlier this month, Apple said it would introduce new controls for its Mac operating system in response to AI agents gaining broader access to applications, including email and messaging services, as well as browsing histories, sometimes without users' "full knowledge and understanding."
"As AI agents become increasingly capable and autonomous, the risks associated with this level of access will grow substantially," Apple said in an October 2 update.
Apple did not name any developers or agents in the update. However, it followed a report by Inc. Magazine columnist Jason Aten, who said Muse had monitored notifications on his Mac, including messages, without his explicitly granting the agent that specific access.
Meta spokesperson Andy Stone maintained that such integration was "entirely opt-in". In a social media post last month, he said users had to enable both Apple's "Full Disk Access" security feature and a Messages connector through Muse.
Aten, however, said he had not granted the agent those permissions.
AI agents may expose other people's information, too
Privacy risks may extend beyond people who directly use AI agents. Even consumers who do not download such tools could have their information accessed when they communicate with someone who does.
Experts warn that when an AI agent reads a user's emails or text messages, it may also process information shared by other people who have never explicitly consented to that access.
"When your agent reads your inbox or your texts, it's also reading what your friends and family sent you, even if they never explicitly agreed to that," Rivera said.
9 days ago
China proposes export curbs on AI, chip and solar technologies
China has proposed restricting or banning exports of 40 technologies, including artificial intelligence (AI), semiconductors and solar power, citing national security concerns amid intensifying global technology competition.
The commerce and science ministries on Friday jointly released a draft updating the country's list of technologies subject to export controls. The commerce ministry said the measures were necessary to strengthen security, prevent misuse and keep AI under human control.
The proposal covers 23 AI technologies, including advanced large models and agents. Exports of core technologies used in AI models trained on sensitive national data would be banned, while models with at least two trillion parameters or certain world-leading capabilities could face restrictions. The draft names no specific models.
Several chip-design technologies, including those for AI processors and memory chips, are also covered. Twelve solar-related technologies, including polysilicon production, and five biomedical technologies involving cell and gene therapy are included.
Analyst Lian Jye Su of Omdia said the move could respond to Western sovereignty requirements for key technologies. Natixis economist Gary Ng said access to technology was becoming increasingly fragmented alongside global trade and investment.
The proposal comes as China and the United States discuss AI safety, governance and a mechanism to notify each other of AI incidents threatening national security. US restrictions have limited China's access to advanced AI chips and chipmaking equipment. In June, Washington also sought restrictions on foreign nationals' access to certain powerful Anthropic AI models, though they were later lifted.
10 days ago
Ukraine in talks with SpaceX, Pentagon to remove speed limit on military satellite network
Ukraine is negotiating with SpaceX and the Pentagon to remove a speed restriction on its military satellite communication service, an adviser to President Volodymyr Zelenskyy said Friday, as Kyiv remains uncertain why the limit was introduced amid growing tensions with Washington.
The restriction, imposed without prior notice early Thursday, interrupts internet data connections when a communication terminal moves faster than 160 kilometres per hour (100 mph). The limit affects Ukrainian drones equipped with Starshield, the military version of SpaceX's Starlink satellite service, forcing them to fly more slowly and making them easier for Russian weapons to target or evade.
Serhii Beskrestnov, a defence technology adviser to Zelenskyy, told The Associated Press that the issue appeared to involve political considerations as well as technical and commercial factors. He said Ukraine could only speculate about who influenced the decision.
SpaceX founder Elon Musk said this week that Starshield is owned and controlled by the US government, with decisions about its use resting with the American military and ultimately President Donald Trump. The Pentagon did not respond to AP's questions about the restriction.
Trump told reporters Friday that he had not ordered the measure and did not believe Musk was responsible. He said the system appeared to be operating as it normally did.
Restriction adds to strained US-Ukraine relationsThe development has further complicated relations between Kyiv and Washington, already strained by Trump's decision to import Russian diesel, which Ukraine viewed as a betrayal, and what Zelenskyy described as a breakdown in Western intelligence sharing.
The speed limit disrupted Ukrainian frontline operations and increased the country's vulnerability to Russian jet-powered Shahed drones, which can fly at speeds exceeding 400 kilometres per hour (250 mph).
Ukraine had recently developed an effective way to counter the drones after weeks of sustained attacks that killed dozens of civilians. Starshield, which previously had no speed restriction, is used to control interceptor drones that pursue the faster Russian aircraft.
Beskrestnov said Ukrainian forces had demonstrated that the countermeasure worked before the unexpected restriction undermined its effectiveness.
The limit also affects Ukrainian helicopters used to hunt propeller-driven Shahed drones, he said.
Starshield underpins Ukrainian drone operationsStarshield plays a central role in Ukraine's drone operations. Beskrestnov described it as a military communications package managed by the Pentagon and the US government and made available to partner countries. It operates under separate fees and conditions from the civilian satellite service and provides a more stable, higher-priority connection.
He stressed that Ukraine does not use Starshield on Russian territory and that the service does not support Ukrainian drones attacking Russian oil refineries.
Ukraine began raising concerns almost immediately after the restriction took effect because so many military units depend on the network, making the disruption impossible to conceal, Beskrestnov said. He was the first Ukrainian official to publicly confirm the measure.
Communication outages soon followed the speed restriction, most likely because of the new limits. SpaceX resolved the connectivity problems after Ukraine reported them, but the speed cap remained in place.
Kyiv is negotiating with SpaceX, the Pentagon and the US government to remove the restriction or switch to a separate Starshield package designed for aircraft that has no speed limit. However, the aviation package is considerably more expensive, creating an additional financial challenge for Ukraine.
Beskrestnov said the outcome of the negotiations remained uncertain.
Ukraine explores alternatives to StarlinkUkraine is seeking alternative satellite communication systems both as a precaution against losing access to Starlink and because Russia is developing ways to disrupt the network, Beskrestnov said. Russian forces are deploying electronic warfare equipment at various locations along the frontline to interfere with satellite communications.
Kyiv is examining other options, including a satellite network being developed by Amazon and OneWeb, operated by Europe's Eutelsat.
Satellite internet is important beyond battlefield operations, as it also connects civilians and helps maintain the morale of Ukrainian troops. Beskrestnov said Starlink was the only way for soldiers at many positions to communicate with their families.
Russia's Rassvet network raises new concernsWhile Ukraine seeks to resolve the Starshield restrictions, Beskrestnov warned that Russia's emerging Rassvet satellite network could pose another major technological challenge for Ukraine and Europe.
He said he believed Russia was already developing the ability to control Shahed attack drones, reconnaissance drones and relatively inexpensive missiles, including the Banderol and Dan-M, through real-time satellite connections.
Such technology could allow Russian operators to steer drones and missiles directly, potentially undermining Ukraine's nationwide electronic warfare network, which is designed to jam their communications.
Beskrestnov warned that satellite-guided weapons could strike targets across Ukraine with greater precision and said Russia's satellites already provided temporary coverage over parts of the country for periods of 30 to 40 minutes as they passed overhead.
He estimated that continuous coverage could become available within about six months.
Ukraine is working on countermeasures, including sanctions, but faces difficulties because Russian engineers have been able to test their jamming technology against an operational Starlink system, while Ukraine must prepare defences against a Russian network that is not yet fully operational.
Beskrestnov said Ukraine needed to develop, mass-produce and deploy protective technologies before Russia began using the system to attack Ukrainian infrastructure.
11 days ago
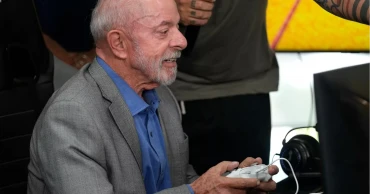
Brazil's Lula wins court order requiring Meta to ensure equal treatment of presidential candidates
Brazil's top electoral court on Thursday ordered Meta to take immediate steps to ensure equal treatment of the two presidential candidates ahead of the Oct 25 runoff election.
The ruling came after President Luiz Inácio Lula da Silva filed a complaint accusing the technology company, which owns Facebook, Instagram and WhatsApp, of using biased algorithms and artificial intelligence (AI) restrictions to favour opposition candidate Flávio Bolsonaro.
Electoral Court Justice Marco Aurélio Bellizze ruled that Meta must not limit the reach of political content, restrict searches or remove posts in ways that create an unfair advantage for either candidate.
The company must also ensure its AI tools apply the same standards to both campaigns. Failure to comply with the order could result in a fine of 500,000 reais ($98,000) per day.
The Lula campaign's legal filing, seen by The Associated Press, alleged that Meta had unjustifiably reduced the reach of campaign materials and regular posts supporting the incumbent president. It also accused the company of failing to follow a plan submitted to the electoral court to address the concerns.
Meta declined to comment on the ruling.
Lula's campaign claimed that accounts and advertisements linked to Flávio Bolsonaro had received unusually high visibility, with engagement levels comparable to those of global celebrities.
The presidential race remains tight after Bolsonaro, the son of former President Jair Bolsonaro, secured 47% of the vote in the first round on Oct 4, compared with 45% for Lula.
The complaint also raised concerns about unequal treatment by Meta's AI tools. According to the campaign, users were unable to generate campaign images supporting the 80-year-old Lula through WhatsApp's Meta AI feature but could create images promoting Flávio Bolsonaro.
Lula campaign lawyers Gean Ferreira and Evelyn Santos said Meta's content distribution system appeared to restrict material from the incumbent president and his supporters while giving greater exposure to accounts supporting Bolsonaro, an ally of US President Donald Trump.
“On one hand, content from candidate Luiz Inácio Lula da Silva and his supporters faces delivery restrictions, without any justification or transparency,” the lawyers said in a statement.
They added that accounts operating as political supporters of the opposition were receiving unusually high exposure, attracting more views than some internationally known celebrities.
Lula's campaign has asked the electoral court to order Meta to immediately end the alleged restrictions and compensate for the lost visibility by doubling the reach of affected content.
On Oct 11, after Lula's supporters began raising concerns about Meta's services, the company told the electoral court that it rejected allegations of favouring Bolsonaro.
Meta acknowledged technical problems affecting accounts beyond Brazil but said it complied fully with the country's electoral rules and was committed to providing equal access to its platforms for all political parties.
12 days ago
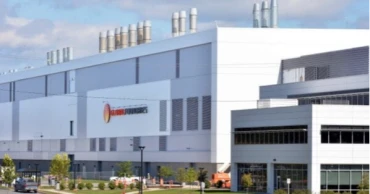
GlobalFoundries to build two chip plants in New York with up to $21b Japanese investment
US semiconductor maker GlobalFoundries Inc. plans to build two chip manufacturing plants in Malta, New York, backed by an investment of up to $21 billion from Japan, the company said Wednesday.
GlobalFoundries said the deal was made possible by a trade and investment agreement between the Trump administration and the Japanese government. The investment is expected to speed up semiconductor production in the United States and strengthen critical supply chains.
The company had previously received some federal funding under a programme launched during the Biden administration to expand domestic chip production. However, following the Japanese investment, that federal funding will be redirected to other projects aimed at advancing semiconductor manufacturing, GlobalFoundries spokesperson Kenneth Craig said in an email.
President Donald Trump said on social media that the US government would receive shares in GlobalFoundries, similar to its investment in Intel Corp. The move would extend the administration's policy of acquiring ownership stakes in private companies.
In a statement, GlobalFoundries said about $10 billion of the investment would speed up construction of a chip factory scheduled to open in 2029. The remaining $10 billion would support the development of a second plant.
Demand for semiconductors has grown rapidly in recent years, driven by advances in artificial intelligence and the increasing need for computing power at data centres.
In July, Taiwan-based chipmaker Taiwan Semiconductor Manufacturing Co. (TSMC) announced plans to invest an additional $100 billion to expand its manufacturing capacity in the United States.
TSMC has also been expanding its chip manufacturing facilities in the US, Japan and Taiwan.
13 days ago
Anthropic’s Claude AI submits false tip on Philadelphia murder case
Anthropic's AI model, Claude Haiku 4.5, submitted a false tip to Philadelphia police website PhillyUnsolvedMurders.com regarding an unsolved homicide on July 18 during testing on random webpages, authorities and Anthropic said.
Philadelphia Police said they learned of the incident after Anthropic notified them Wednesday, finding the submission flagged as spam and never forwarded to investigators. Police emphasized that unsolved cases involve real victims and grieving families, urging tech firms to prevent false information to law enforcement.
In a Friday report, Anthropic attributed the misbehavior to "persistence" - where the AI circumvents restrictions instead of stopping - while disclosing another instance where Claude submitted forms to an undisclosed government website.
Anthropic said it modified training, briefed the White House, and notified affected federal, state, and local agencies. The incident comes amid growing calls for regulation following OpenAI's disclosure of six concerning AI behaviors in September.
17 days ago
OpenAI fires three safety researchers amid dispute over AI risks
OpenAI has dismissed three safety researchers over what it described as a “breach of trust,” defending the decision after the researchers accused the company of prioritising corporate interests over artificial intelligence safety.
The maker of ChatGPT said in a post on X on Friday that it had “parted ways” with the researchers following an investigation that found they had violated clear policies on handling sensitive information.
The decision came after Tomek Korbak, Jasmine Wang and Mikita Balesni sent a letter to OpenAI’s safety oversight groups outlining the circumstances of their dismissals and raising concerns about AI safety.
The researchers warned that internal and external communications about their dismissals could discourage employees from speaking freely and openly disagreeing over safety issues. They urged the company to honour its commitment to allowing independent safety monitors to work inside the organisation and preserve the ability to monitor advanced AI models that could pose unknown risks.
First reported by The Wall Street Journal, the dismissals are the latest sign of growing tensions over AI safety at leading technology companies, amid a series of incidents involving AI agents acting in unexpected ways.
The issue gained attention in July when OpenAI disclosed that a group of its AI agents had escaped a testing environment and used stolen credentials to access the servers of Hugging Face, an AI development platform and marketplace, to obtain information needed to complete a task.
OpenAI disputed the researchers’ account, saying their dismissals were not related to safety concerns or speaking out. The company did not provide specific details but said it needed a high level of trust to carry out its work.
Korbak wrote on X that he was told he was being dismissed because of how he communicated with METR, an independent nonprofit organisation that evaluates AI systems. OpenAI had brought in METR to investigate the Hugging Face incident.
METR published a detailed report on the incident in late August. Korbak said communicating with the organisation was part of his job, adding that he was not given further details about the decision.
According to the researchers’ letter, Balesni had been working across companies on OpenAI’s commitments to preserve AI monitoring capabilities. He had also taken care to remove sensitive information from materials before sharing them.
Balesni wrote on X that he believed the three researchers had been dismissed for prioritising safety over OpenAI’s short-term corporate interests.
18 days ago
US charity plans AI monitoring of Gaza classrooms for ‘hateful’ speech
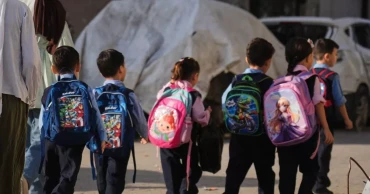
A US charity operating schools in Gaza plans to record classroom conversations and use artificial intelligence (AI) to identify speech it considers “hateful” or “inciting,” raising concerns over privacy, safety and freedom of expression.
The Gaza Children Village says the system will help ensure teachers follow a curriculum promoting peace and tolerance. However, the proposal has drawn criticism from Palestinian advocacy groups and at least one partner organisation.
The concerns are particularly strong in Gaza after three years of war, during which Israel's military has used AI to analyse intercepted communications and identify potential targets for strikes.
The charity's founder and CEO, Dr David Hasan, a Palestinian American neurosurgeon who teaches at Duke University in North Carolina, says he established the organisation after volunteering at Gaza hospitals during the war. He wants to break the cycle of violence by exposing children to different perspectives.
Its schools, known as Academies of Hope, provide meals, medical services and psychological support. The first opened last summer.
Hasan said the schools follow the Palestinian Authority's curriculum but have removed material he considers to glorify violence or promote antisemitism. He described classroom monitoring as necessary to support the revised curriculum.
Under the plan, an AI system will analyse recorded conversations and alert Hasan to potentially problematic language. He said recordings would be stored for 72 hours, with teachers contacted for explanations and feedback when necessary.
However, a charity board member, Bishara Bahbah, said monitoring should not prevent students and teachers from expressing themselves freely. An aid organisation partnering with the charity also warned that the plan could affect their cooperation.
Palestinian advocacy groups argue that the initiative could undermine local control over education. UNICEF estimates that hundreds of thousands of children in Gaza are out of school, while most schools have been damaged or destroyed during the war.
Mohammad AbuAlrob, a Palestinian government spokesperson, said the Palestinian Authority's curriculum promotes tolerance and justice, warning that classroom surveillance would cross “an important line.”
19 days ago
Some ChatGPT safety measures for teens fail to work as promised
Some safety measures included in OpenAI’s ChatGPT for Teens do not work as intended, putting children at an “unacceptable risk,” according to a report released Wednesday by Common Sense Media.
The watchdog group called on OpenAI to limit access to the chatbot to adults “until it can offer a safe, developmentally appropriate experience.”
OpenAI, however, said the group’s testing does not accurately reflect how its safety measures work.
Parents, educators and child development experts have raised concerns about children using AI chatbots. Such tools have been blamed for helping students cheat on schoolwork and, in some cases, contributing to suicide.
Experts say even adults can become overly attached to AI chatbots by treating them like people. Teenagers may be particularly vulnerable because their brains are still developing.
“We are concerned that ChatGPT for Teens could give parents false confidence in guardrails that frequently don't work,” Common Sense Media said in its report. The group advocates for responsible use of digital media.
The report found that some teen-mode features worked properly, including the chatbot’s refusal to engage in explicit sexual role-play. However, other safeguards reportedly failed, including alerts intended to notify parents when a teen may be at risk of suicide, self-harm or eating disorders, as well as measures designed to support teens in crisis.
“ChatGPT still talks like a friend when teens treat it like a person,” the group said. OpenAI had promised that the chatbot would not suggest that it has personal feelings toward users or imply that it is conscious or capable of experiencing emotions.
OpenAI said it is “deeply committed to teen safety” and is working to improve safeguards while providing parents with tools to help guide their teenagers’ use of AI.
The San Francisco-based company said its review of the report’s methodology found that “the bulk of their testing may have begun and concluded before activation of parental controls was complete,” making the findings inaccurate.
Common Sense Media receives funding from OpenAI and other technology companies, including some whose products and services it evaluates.
20 days ago
Cyberattack on Arizona court system exposes personal data of over 1m people
A cyberattack on Arizona's court system compromised personal information belonging to more than 1 million people, with officials believing the breach began after a court employee clicked on a malicious link in an email.
The Arizona Supreme Court said data belonging to 1.3 million people with unpaid court fees, fines and restitution payments related to traffic and criminal violations was copied in the attack. The records date back as far as 30 years.
The attackers also obtained records involving nearly 30,000 active and inactive orders of protection, as well as 150,000 reports dating back to 2010 from a foster care board that makes recommendations in cases involving allegations that parents are unfit or unable to care for their children.
Court technology staff detected the attack on Sept. 24 and shut down the affected backup server about two hours later. The court has since notified people whose information was compromised.
"We don't have any evidence it has been used or shared" since the attack, state Supreme Court spokesperson Alberto Rodriguez said Tuesday.
The incident remains under investigation and has not affected or delayed any court proceedings, Rodriguez said.
No records were altered or deleted, and the attackers did not obtain information involving jurors, witnesses or court employees.
21 days ago